In 2025 the card networks and the large platforms shipped the rails for agentic commerce: Visa Intelligent Commerce and Mastercard Agent Pay in April, Google’s Agent Payments Protocol in September, Visa’s Trusted Agent Protocol in October. In June 2026 Mastercard extended Agent Pay to machine counterparties. The infrastructure for software to transact on a customer’s behalf now exists. The control framework to govern it does not.
An agent is a delegation, not a customer
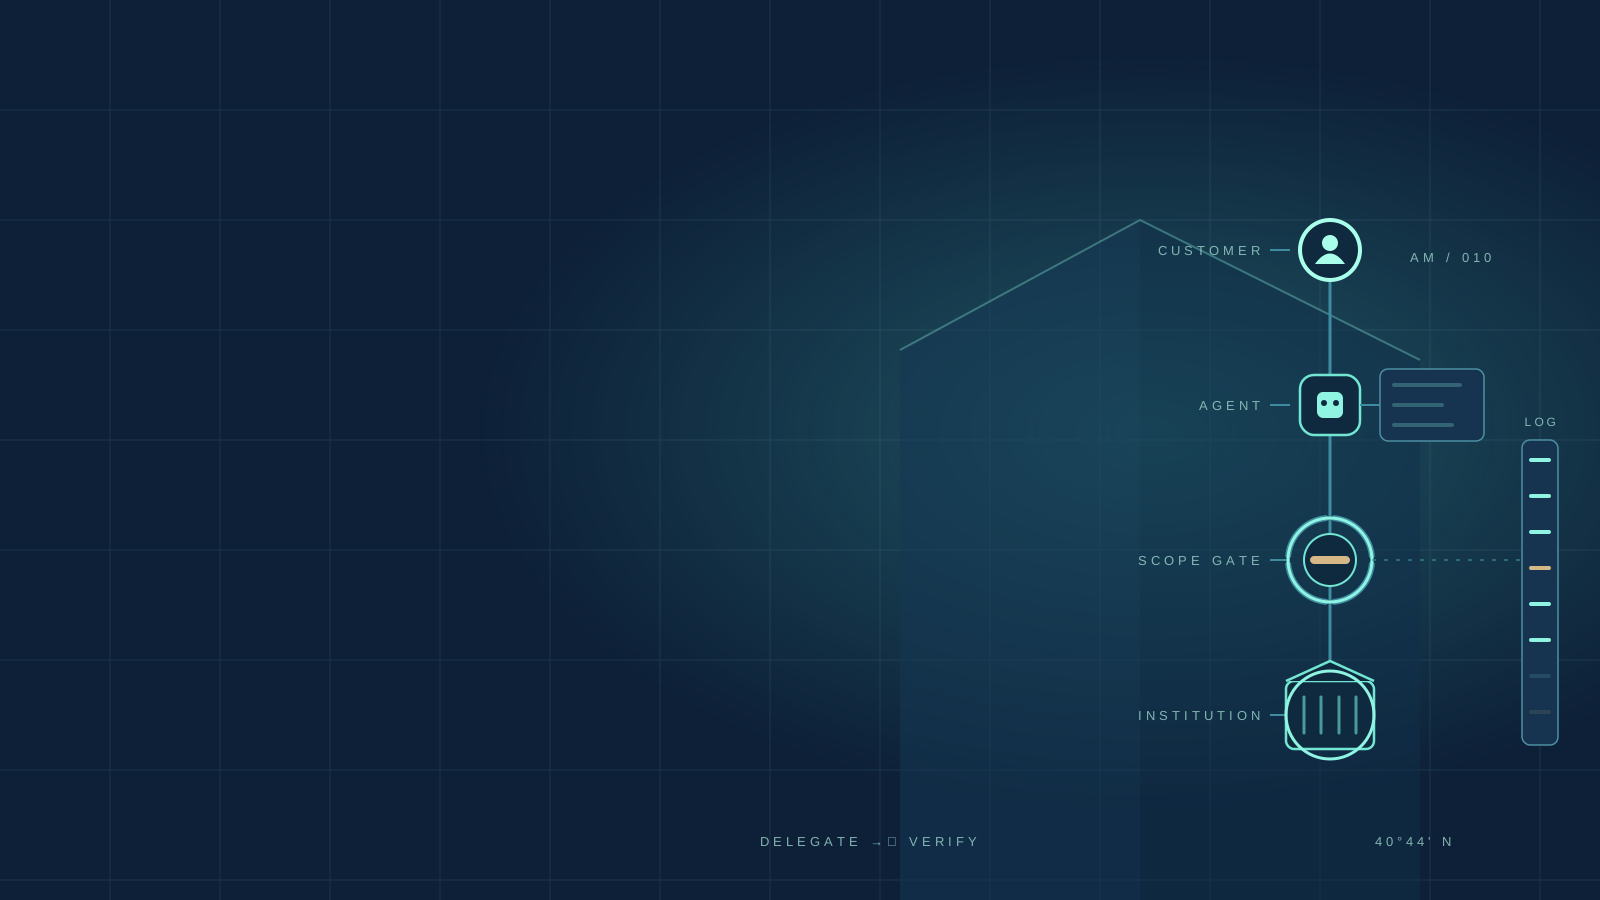
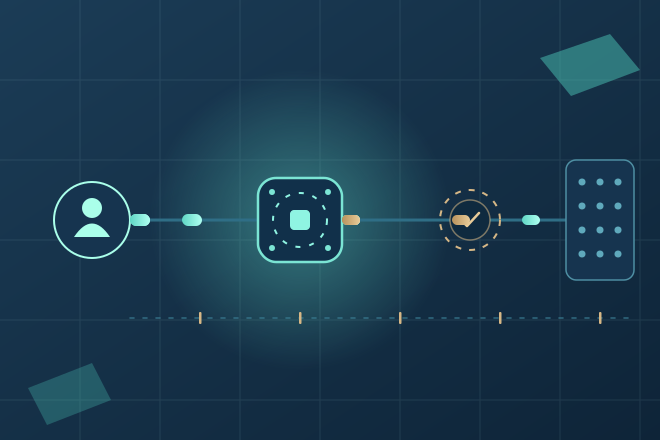
The instinct is to treat an AI agent as a new kind of customer and run it through onboarding. That is the wrong frame. An agent arrives already attached to a customer the institution knows. The question is not who the agent is but what it has been authorized to do, by whom, within what limits, and whether that authority is still valid at the moment it acts. Know Your Agent, as the term is being used across the industry, collects those questions under one heading: who authorized this action, what is this agent permitted to do, and should it be permitted to do it right now.
What changes from KYC
KYC verifies a reasonably stable identity once and monitors it over time. An agent’s authority can change by session, by task and by principal. The same agent may be allowed to check a balance in the morning and barred from initiating a payment in the afternoon because its mandate changed. Verification therefore has to be continuous rather than periodic, and scope has to be enforced at the point of action rather than assumed from the fact of a login.
There is a second difference. A person’s behavior is their own. An agent’s behavior is a blend of its instructions, its model and whatever it has been exposed to, and it can be redirected by content it reads. Behavioral monitoring has to baseline the agent separately from the human it serves, and an agent with perfectly valid credentials that starts behaving unlike itself is a signal, not a false positive.
What a bank is actually obliged to do today
Less than the volume of commentary suggests, and more than nothing. No regulator in the United States has adopted a Know Your Agent rule, and there is no KYA obligation to be compliant with. What exists is a set of obligations already in force that an agent-initiated transaction lands on: customer identification under 31 CFR 1020.220, beneficial ownership under 1010.230, recordkeeping under 1010.410, and UCC Article 4A for commercial funds transfers. The agent cannot be the customer for Bank Secrecy Act purposes. The entity that deploys it is, and that is where the obligation sits.
The closest supervisory hook is the FFIEC guidance on authentication and access to financial institution services, which sets expectations for controls over customer information and transaction capability without regard to whether the request comes from a person or from software. NIST’s National Cybersecurity Center of Excellence issued a concept paper on agent identity and authorization in February 2026 that frames the governance questions well and answers none of them. In the European Union, the transparency duties in Article 50 of the AI Act are the clearest reach to consumer-facing agents.
It is worth saying plainly that much of what is published under the Know Your Agent label is vendor material for identity products, and several of the frameworks on offer are a single firm’s taxonomy presented as a standard. The problem is real. The consensus on how to solve it is thinner than the volume of content implies.
The liability question nobody has answered
Consumer protections under Regulation E and the Truth in Lending Act turn on a transfer being unauthorized. If a customer handed an agent their credentials and the agent did something the customer did not intend, it is not obvious the transfer was unauthorized in the statutory sense, which would leave the consumer with exposure the statutes never contemplated. On the commercial side, under UCC Article 4A, if an agent’s signing credentials are held to be a commercially reasonable security procedure, loss can shift to the corporate customer. Neither question has been tested. For an institution, the exposure sits in that gap more than in any framework.
The controls that make sense
Across the material that is credible, the same five layers recur, and they are sensible whatever label they end up carrying. Detect that an agent is present and validate its credentials and deployment source. Trace the authorization chain back to a responsible principal and confirm that the scope granted is the scope being exercised. Enforce limits on what the agent can do, spend and for how long, dynamically rather than once at login. Baseline the agent’s behavior separately from its human and treat deviation as a signal even when credentials check out. Keep a person in the loop for high-risk actions, with an audit trail showing what was done, when, under whose authority and who is accountable.
None of that is exotic. Most of it maps onto controls an institution already operates for human customers and third parties. The work is in deciding where an agent fits into those controls, which is a process question before it is a technology one.
Where to start
Treat it as an operating model and controls problem first. Establish where agents already touch your channels, because they do, whether or not anyone has declared them. Measure what passes through today and under what authority. Prioritize by exposure: payment initiation before balance enquiry, commercial before retail if your Article 4A posture is unclear. Design the scope and authorization controls into the existing authentication and fraud stack rather than beside it. Then prove the controls work and keep the evidence, because the examiner’s question will be the one it has always been: show me the controls over access to customer data and transaction capability.
That sequence is the one we apply to any new control domain, and it is why this question sits at the intersection of two things we already do: KYC operating model work and AI governance.
How EPIF sequences a new control domain
Governed AI deployment: use cases, evidence and oversight
The future of KYC is a better process
COMMON QUESTIONS
Know Your Agent, answered.
The questions compliance and risk teams raise first.
No. No regulator in the United States has adopted a Know Your Agent rule. The obligations an agent-initiated transaction lands on already exist: customer identification, beneficial ownership and recordkeeping under the Bank Secrecy Act rules, UCC Article 4A for commercial funds transfers, and the FFIEC guidance on authentication and access. KYA is a way of organizing those obligations for a new kind of actor.
KYC verifies a reasonably stable identity once and monitors it. An agent is a delegation from a customer the institution already knows, whose authority can change by session, task and principal. The control question shifts from who this is to what it is authorized to do, by whom, within what limits, and whether that authority is still valid at the moment it acts. Verification becomes continuous and scope is enforced at the point of action.
Unresolved. Consumer protections under Regulation E and the Truth in Lending Act turn on a transfer being unauthorized, and it is not settled whether a transfer by an agent the customer credentialed qualifies. For commercial wires under UCC Article 4A, if the agent’s credentials are held to be a commercially reasonable security procedure, loss can shift to the corporate customer. Neither question has been tested.
Find where agents already touch your channels, because they do whether or not anyone has declared them. Measure what passes through today and under what authority. Prioritize by exposure, payment initiation before balance inquiry. Design scope and authorization controls into the existing authentication and fraud stack rather than beside it. Then prove the controls work and keep the evidence.